


Why are all links in GD going through sovrn.co now? (Page 2 of 2)

|
Originally Posted By MongooseKY: I'm using TamperMonkey with the following script to eradicate sovrn, vigilink, and avantlink redirects across the board. I'm sick and tired of being monetized by having everything I click routed through third parties who aren't accountable for the crap they do. // ==UserScript== // @name Remove VigLink, AvantLink, and Sovrn Redirects // @namespace https://tampermonkey.net/ // @version 1.0 // @description Strip redirect wrappers from VigLink, AvantLink, and Sovrn links // @match *://*/* // @run-at document-end // @grant none // ==/UserScript== (function() { 'use strict'; const REDIRECT_DOMAINS = [ "viglink.com", "redirect.viglink.com", "avantlink.com", "www.avantlink.com", "sovrn.co", "redirect.sovrn.com" ]; const PARAM_CANDIDATES = [ "url", "u", "dest", "destination", "to", "afsrc", "redir", "r" ]; function extractRealUrl(href) { try { const parsed = new URL(href); // Check if this is a redirector domain if (!REDIRECT_DOMAINS.some(d => parsed.hostname.includes(d))) { return null; } // Try all known parameter names for (const p of PARAM_CANDIDATES) { let val = parsed.searchParams.get(p); if (val) { // Some redirectors double-encode URLs try { val = decodeURIComponent(val); } catch {} try { val = decodeURIComponent(val); } catch {} // Validate it's a real URL if (val.startsWith("http://") || val.startsWith("https://")) { return val; } } } return null; } catch (e) { console.error("Redirect fix error:", e); return null; } } function fixLink(a) { if (!a || !a.href) return; const real = extractRealUrl(a.href); if (real) { console.log("Rewriting URL: " + a.href + " as " + real); a.href = real; } } function scan() { document.querySelectorAll("a[href]").forEach(fixLink); } // Initial scan scan(); // Watch for dynamically added links const observer = new MutationObserver(mutations => { for (const m of mutations) { for (const node of m.addedNodes) { if (node.nodeType === 1) { if (node.tagName === "A") { fixLink(node); } else { node.querySelectorAll?.("a[href]").forEach(fixLink); } } } } }); observer.observe(document.body, { childList: true, subtree: true }); })(); I love how the domains in your script even got sovrn'd. 
|


|
Originally Posted By laxman09: tagging by for easy fixes that dont require me to know how to code I noticed the redirects the other day and stopped clicking on links because it looks suspicious. Originally Posted By laxman09: tagging by for easy fixes that dont require me to know how to code I noticed the redirects the other day and stopped clicking on links because it looks suspicious. You don't need to code. Claude Code, free version, no subscription: I want to code a chrome extension I can add to Brave Browser for ar15.com to sanitize their affiliate links. When you post a link, they run it through a few different things to monetize it. Examples: Actual link: https://www.amazon.com/Chicken-Sea-Imitation-Crabmeat-Packet/dp/B0FH775YW6 Monetized link: https://www.amazon.com/dp/B0FH775YW6?tag=arfcom00-20 Actual link: https://yahoo.com Monetized link: https://sovrn.co/?key=41eb5962625ae87b4762e5bd8c88faf6&u=https%3A%2F%2Fwww%2Eyahoo%2Ecom%2F&cuid=52825 For both types of link monetization, I want the link when I click on it to take me to the actual link, not pass through the monetized link. |

|
Originally Posted By Dangus: I love how the domains in your script even got sovrn'd. |
01010111 | 57 | 127 | LXXXVII
Joined:
Jul 2023
Posts:
3686
EE: 0% (0)
 FL, USA
|
Originally Posted By MongooseKY: I'm using TamperMonkey with the following script to eradicate sovrn, vigilink, and avantlink redirects across the board. I'm sick and tired of being monetized by having everything I click routed through third parties who aren't accountable for the crap they do. // ==UserScript== // @name Remove VigLink, AvantLink, and Sovrn Redirects // @namespace https://tampermonkey.net/ // @version 1.0 // @description Strip redirect wrappers from VigLink, AvantLink, and Sovrn links // @match *://*/* // @run-at document-end // @grant none // ==/UserScript== (function() { 'use strict'; const REDIRECT_DOMAINS = [ "viglink.com", "redirect.viglink.com", "avantlink.com", "www.avantlink.com", "sovrn.co", "redirect.sovrn.com" ]; const PARAM_CANDIDATES = [ "url", "u", "dest", "destination", "to", "afsrc", "redir", "r" ]; function extractRealUrl(href) { try { const parsed = new URL(href); // Check if this is a redirector domain if (!REDIRECT_DOMAINS.some(d => parsed.hostname.includes(d))) { return null; } // Try all known parameter names for (const p of PARAM_CANDIDATES) { let val = parsed.searchParams.get(p); if (val) { // Some redirectors double-encode URLs try { val = decodeURIComponent(val); } catch {} try { val = decodeURIComponent(val); } catch {} // Validate it's a real URL if (val.startsWith("http://") || val.startsWith("https://")) { return val; } } } return null; } catch (e) { console.error("Redirect fix error:", e); return null; } } function fixLink(a) { if (!a || !a.href) return; const real = extractRealUrl(a.href); if (real) { console.log("Rewriting URL: " + a.href + " as " + real); a.href = real; } } function scan() { document.querySelectorAll("a[href]").forEach(fixLink); } // Initial scan scan(); // Watch for dynamically added links const observer = new MutationObserver(mutations => { for (const m of mutations) { for (const node of m.addedNodes) { if (node.nodeType === 1) { if (node.tagName === "A") { fixLink(node); } else { node.querySelectorAll?.("a[href]").forEach(fixLink); } } } } }); observer.observe(document.body, { childList: true, subtree: true }); })(); This version retains the original script's simple purpose but makes it substantially safer and more reliable. Most importantly, it replaces the loose hostname.includes() test with strict domain/subdomain matching, so a domain such as viglink.com.malicious-site.com cannot be mistaken for VigLink. It also safely validates that extracted destinations are genuine http:// or https:// URLs, avoids unnecessarily decoding already-valid URLs, performs case-insensitive parameter matching, and can unwrap several nested affiliate redirects. In addition to scanning the page when it loads, it now watches both new links and existing links whose href is changed later by JavaScript, and it performs another check immediately when a link is clicked. It still uses @grant none, makes no external network requests, loads no outside code, and sends no information anywhere. The original script's basic behavior and scope are preserved while addressing the weaknesses I found in its domain matching, decoding, and dynamic-link handling. // ==UserScript== // @name Remove VigLink, AvantLink, and Sovrn Redirects // @namespace https://tampermonkey.net/ // @version 2.0 // @description Replace VigLink, AvantLink, and Sovrn affiliate redirect links with their direct destination URLs // @match *://*/* // @run-at document-end // @grant none // ==/UserScript== (function () { 'use strict'; /* * Redirect networks to remove. * * Matching is restricted to the actual domain or one of its subdomains. * Example: * redirect.viglink.com -> matches * viglink.com -> matches * viglink.com.evilsite.com -> does NOT match */ const REDIRECT_DOMAINS = [ 'viglink.com', 'avantlink.com', 'sovrn.com', 'sovrn.co' ]; /* * Common query-string parameters used to hold the real destination URL. */ const PARAM_CANDIDATES = new Set([ 'url', 'u', 'dest', 'destination', 'to', 'afsrc', 'redir', 'redirect', 'redirecturl', 'target', 'r' ]); /* * Set to true if you want rewritten links displayed in the browser console. */ const DEBUG = false; function log(...args) { if (DEBUG) { console.log('[Affiliate Redirect Remover]', ...args); } } /* * Strictly determine whether a hostname belongs to one of the * redirect networks. */ function isRedirectDomain(hostname) { if (!hostname) return false; const host = hostname.toLowerCase().replace(/\.$/, ''); return REDIRECT_DOMAINS.some(domain => host === domain || host.endsWith('.' + domain) ); } /* * Only permit normal HTTP/HTTPS destination URLs. */ function isValidHttpUrl(value) { if (!value || typeof value !== 'string') { return false; } try { const parsed = new URL(value); return parsed.protocol === 'http:' || parsed.protocol === 'https:'; } catch { return false; } } /* * URLSearchParams already performs one level of decoding. * * Only decode again when the current value is NOT already a valid URL. * This prevents legitimate encoded characters inside the destination URL * from being unnecessarily decoded. */ function normalizeDestination(value) { if (!value) return null; let candidate = value.trim(); if (isValidHttpUrl(candidate)) { return candidate; } for (let i = 0; i < 2; i++) { try { const decoded = decodeURIComponent(candidate); if (decoded === candidate) { break; } candidate = decoded; if (isValidHttpUrl(candidate)) { return candidate; } } catch { break; } } return null; } /* * Extract the real destination URL from one redirect wrapper. */ function extractDestination(href) { try { const parsed = new URL(href); if (!isRedirectDomain(parsed.hostname)) { return null; } /* * Parameter matching is case-insensitive. */ for (const [key, value] of parsed.searchParams.entries()) { if (!PARAM_CANDIDATES.has(key.toLowerCase())) { continue; } const destination = normalizeDestination(value); if (destination) { return destination; } } return null; } catch (error) { log('Unable to parse URL:', href, error); return null; } } /* * Unwrap multiple redirect layers if one affiliate redirect points * through another supported affiliate redirect. * * The depth limit prevents malformed links from creating a loop. */ function unwrapRedirect(href, maxDepth = 5) { let current = href; let changed = false; const seen = new Set(); for (let depth = 0; depth < maxDepth; depth++) { if (seen.has(current)) { break; } seen.add(current); const destination = extractDestination(current); if (!destination || destination === current) { break; } current = destination; changed = true; } return changed ? current : null; } /* * Rewrite an individual link. */ function fixLink(link) { if (!(link instanceof HTMLAnchorElement)) { return; } const href = link.href; if (!href) { return; } const directUrl = unwrapRedirect(href); if (directUrl && directUrl !== href) { log('Rewriting:', href, '->', directUrl); link.href = directUrl; } } /* * Scan all links currently present on the page. */ function scan(root = document) { if (!root?.querySelectorAll) { return; } root.querySelectorAll('a[href]').forEach(fixLink); } /* * Initial page scan. */ scan(); /* * Catch links immediately before the user interacts with them. * * This provides another layer of protection against sites that rewrite * links shortly before a click. */ function fixClickedLink(event) { const target = event.target; if (!(target instanceof Element)) { return; } const link = target.closest('a[href]'); if (link) { fixLink(link); } } document.addEventListener('pointerdown', fixClickedLink, true); document.addEventListener('click', fixClickedLink, true); /* * Watch for: * * 1. New links added dynamically. * 2. Existing links whose href attribute is changed after page load. */ const observer = new MutationObserver(mutations => { for (const mutation of mutations) { if ( mutation.type === 'attributes' && mutation.target instanceof HTMLAnchorElement ) { fixLink(mutation.target); continue; } if (mutation.type === 'childList') { for (const node of mutation.addedNodes) { if (!(node instanceof Element)) { continue; } if (node instanceof HTMLAnchorElement) { fixLink(node); } scan(node); } } } }); observer.observe(document.documentElement, { childList: true, subtree: true, attributes: true, attributeFilter: ['href'] }); })(); |


|
Originally Posted By Trump45: // ==UserScript== // @name Remove VigLink, AvantLink, and Sovrn Redirects // @namespace https://tampermonkey.net/ // @version 2.0 // @description Replace VigLink, AvantLink, and Sovrn affiliate redirect links with their direct destination URLs // @match *://*/* // @run-at document-end // @grant none // ==/UserScript== (function () { 'use strict'; /* * Redirect networks to remove. * * Matching is restricted to the actual domain or one of its subdomains. * Example: * redirect.viglink.com -> matches * viglink.com -> matches * viglink.com.evilsite.com -> does NOT match */ const REDIRECT_DOMAINS = [ 'viglink.com', 'avantlink.com', 'sovrn.com', 'sovrn.co' ]; /* * Common query-string parameters used to hold the real destination URL. */ const PARAM_CANDIDATES = new Set([ 'url', 'u', 'dest', 'destination', 'to', 'afsrc', 'redir', 'redirect', 'redirecturl', 'target', 'r' ]); /* * Set to true if you want rewritten links displayed in the browser console. */ const DEBUG = false; function log(...args) { if (DEBUG) { console.log('[Affiliate Redirect Remover]', ...args); } } /* * Strictly determine whether a hostname belongs to one of the * redirect networks. */ function isRedirectDomain(hostname) { if (!hostname) return false; const host = hostname.toLowerCase().replace(/\.$/, ''); return REDIRECT_DOMAINS.some(domain => host === domain || host.endsWith('.' + domain) ); } /* * Only permit normal HTTP/HTTPS destination URLs. */ function isValidHttpUrl(value) { if (!value || typeof value !== 'string') { return false; } try { const parsed = new URL(value); return parsed.protocol === 'http:' || parsed.protocol === 'https:'; } catch { return false; } } /* * URLSearchParams already performs one level of decoding. * * Only decode again when the current value is NOT already a valid URL. * This prevents legitimate encoded characters inside the destination URL * from being unnecessarily decoded. */ function normalizeDestination(value) { if (!value) return null; let candidate = value.trim(); if (isValidHttpUrl(candidate)) { return candidate; } for (let i = 0; i < 2; i++) { try { const decoded = decodeURIComponent(candidate); if (decoded === candidate) { break; } candidate = decoded; if (isValidHttpUrl(candidate)) { return candidate; } } catch { break; } } return null; } /* * Extract the real destination URL from one redirect wrapper. */ function extractDestination(href) { try { const parsed = new URL(href); if (!isRedirectDomain(parsed.hostname)) { return null; } /* * Parameter matching is case-insensitive. */ for (const [key, value] of parsed.searchParams.entries()) { if (!PARAM_CANDIDATES.has(key.toLowerCase())) { continue; } const destination = normalizeDestination(value); if (destination) { return destination; } } return null; } catch (error) { log('Unable to parse URL:', href, error); return null; } } /* * Unwrap multiple redirect layers if one affiliate redirect points * through another supported affiliate redirect. * * The depth limit prevents malformed links from creating a loop. */ function unwrapRedirect(href, maxDepth = 5) { let current = href; let changed = false; const seen = new Set(); for (let depth = 0; depth < maxDepth; depth++) { if (seen.has(current)) { break; } seen.add(current); const destination = extractDestination(current); if (!destination || destination === current) { break; } current = destination; changed = true; } return changed ? current : null; } /* * Rewrite an individual link. */ function fixLink(link) { if (!(link instanceof HTMLAnchorElement)) { return; } const href = link.href; if (!href) { return; } const directUrl = unwrapRedirect(href); if (directUrl && directUrl !== href) { log('Rewriting:', href, '->', directUrl); link.href = directUrl; } } /* * Scan all links currently present on the page. */ function scan(root = document) { if (!root?.querySelectorAll) { return; } root.querySelectorAll('a[href]').forEach(fixLink); } /* * Initial page scan. */ scan(); /* * Catch links immediately before the user interacts with them. * * This provides another layer of protection against sites that rewrite * links shortly before a click. */ function fixClickedLink(event) { const target = event.target; if (!(target instanceof Element)) { return; } const link = target.closest('a[href]'); if (link) { fixLink(link); } } document.addEventListener('pointerdown', fixClickedLink, true); document.addEventListener('click', fixClickedLink, true); /* * Watch for: * * 1. New links added dynamically. * 2. Existing links whose href attribute is changed after page load. */ const observer = new MutationObserver(mutations => { for (const mutation of mutations) { if ( mutation.type === 'attributes' && mutation.target instanceof HTMLAnchorElement ) { fixLink(mutation.target); continue; } if (mutation.type === 'childList') { for (const node of mutation.addedNodes) { if (!(node instanceof Element)) { continue; } if (node instanceof HTMLAnchorElement) { fixLink(node); } scan(node); } } } }); observer.observe(document.documentElement, { childList: true, subtree: true, attributes: true, attributeFilter: ['href'] }); })(); Brave for desktop can take this script above with no add-ons or plugins. It has native support for "Scriptlets" if Developer Mode is enabled. I figured this out after being annoyed at not being able to clearly see the target URL due to the restructuring of the link with the click tracker. Also as mentioned copying a link to share or bookmark was picking up this BS sovrn url with it depending how it was manipulated. Go to the settings page by pasting this into the URL box: brave://settings/shields/filters Scroll down and toggle on the "Developer Mode" Create custom filter: ar15.com##+js(user-sovrn-direct.js) and Save.Then "Add new scriptlet" and name it: sovrn-direct Then paste in the script from the post I quoted and save all that. Refresh browser...... |
|
Originally Posted By Piratepast40: Really not sure if I'm supposed to care about this or not. Since I'm an ARF/GD bazillionaire with a wife sporting vodknockers, guess I'll subscribe and let one of my minions see if it's important. Given it's going to fingerprint you and your online activity to arfcom at some level it's probably more meaningful than driving past a flock camera lol. |
|
Originally Posted By Cobalt135: Brave for desktop can take this script above with no add-ons or plugins. It has native support for "Scriptlets" if Developer Mode is enabled. I figured this out after being annoyed at not being able to clearly see the target URL due to the restructuring of the link with the click tracker. Also as mentioned copying a link to share or bookmark was picking up this BS sovrn url with it depending how it was manipulated. Go to the settings page by pasting this into the URL box: brave://settings/shields/filters Scroll down and toggle on the "Developer Mode" Create custom filter: ar15.com##+js(user-sovrn-direct.js) and Save.Then "Add new scriptlet" and name it: sovrn-direct Then paste in the script from the post I quoted and save all that. Refresh browser...... Originally Posted By Cobalt135: Originally Posted By Trump45: // ==UserScript== // @name Remove VigLink, AvantLink, and Sovrn Redirects // @namespace https://tampermonkey.net/ // @version 2.0 // @description Replace VigLink, AvantLink, and Sovrn affiliate redirect links with their direct destination URLs // @match *://*/* // @run-at document-end // @grant none // ==/UserScript== (function () { 'use strict'; /* * Redirect networks to remove. * * Matching is restricted to the actual domain or one of its subdomains. * Example: * redirect.viglink.com -> matches * viglink.com -> matches * viglink.com.evilsite.com -> does NOT match */ const REDIRECT_DOMAINS = [ 'viglink.com', 'avantlink.com', 'sovrn.com', 'sovrn.co' ]; /* * Common query-string parameters used to hold the real destination URL. */ const PARAM_CANDIDATES = new Set([ 'url', 'u', 'dest', 'destination', 'to', 'afsrc', 'redir', 'redirect', 'redirecturl', 'target', 'r' ]); /* * Set to true if you want rewritten links displayed in the browser console. */ const DEBUG = false; function log(...args) { if (DEBUG) { console.log('[Affiliate Redirect Remover]', ...args); } } /* * Strictly determine whether a hostname belongs to one of the * redirect networks. */ function isRedirectDomain(hostname) { if (!hostname) return false; const host = hostname.toLowerCase().replace(/\.$/, ''); return REDIRECT_DOMAINS.some(domain => host === domain || host.endsWith('.' + domain) ); } /* * Only permit normal HTTP/HTTPS destination URLs. */ function isValidHttpUrl(value) { if (!value || typeof value !== 'string') { return false; } try { const parsed = new URL(value); return parsed.protocol === 'http:' || parsed.protocol === 'https:'; } catch { return false; } } /* * URLSearchParams already performs one level of decoding. * * Only decode again when the current value is NOT already a valid URL. * This prevents legitimate encoded characters inside the destination URL * from being unnecessarily decoded. */ function normalizeDestination(value) { if (!value) return null; let candidate = value.trim(); if (isValidHttpUrl(candidate)) { return candidate; } for (let i = 0; i < 2; i++) { try { const decoded = decodeURIComponent(candidate); if (decoded === candidate) { break; } candidate = decoded; if (isValidHttpUrl(candidate)) { return candidate; } } catch { break; } } return null; } /* * Extract the real destination URL from one redirect wrapper. */ function extractDestination(href) { try { const parsed = new URL(href); if (!isRedirectDomain(parsed.hostname)) { return null; } /* * Parameter matching is case-insensitive. */ for (const [key, value] of parsed.searchParams.entries()) { if (!PARAM_CANDIDATES.has(key.toLowerCase())) { continue; } const destination = normalizeDestination(value); if (destination) { return destination; } } return null; } catch (error) { log('Unable to parse URL:', href, error); return null; } } /* * Unwrap multiple redirect layers if one affiliate redirect points * through another supported affiliate redirect. * * The depth limit prevents malformed links from creating a loop. */ function unwrapRedirect(href, maxDepth = 5) { let current = href; let changed = false; const seen = new Set(); for (let depth = 0; depth < maxDepth; depth++) { if (seen.has(current)) { break; } seen.add(current); const destination = extractDestination(current); if (!destination || destination === current) { break; } current = destination; changed = true; } return changed ? current : null; } /* * Rewrite an individual link. */ function fixLink(link) { if (!(link instanceof HTMLAnchorElement)) { return; } const href = link.href; if (!href) { return; } const directUrl = unwrapRedirect(href); if (directUrl && directUrl !== href) { log('Rewriting:', href, '->', directUrl); link.href = directUrl; } } /* * Scan all links currently present on the page. */ function scan(root = document) { if (!root?.querySelectorAll) { return; } root.querySelectorAll('a[href]').forEach(fixLink); } /* * Initial page scan. */ scan(); /* * Catch links immediately before the user interacts with them. * * This provides another layer of protection against sites that rewrite * links shortly before a click. */ function fixClickedLink(event) { const target = event.target; if (!(target instanceof Element)) { return; } const link = target.closest('a[href]'); if (link) { fixLink(link); } } document.addEventListener('pointerdown', fixClickedLink, true); document.addEventListener('click', fixClickedLink, true); /* * Watch for: * * 1. New links added dynamically. * 2. Existing links whose href attribute is changed after page load. */ const observer = new MutationObserver(mutations => { for (const mutation of mutations) { if ( mutation.type === 'attributes' && mutation.target instanceof HTMLAnchorElement ) { fixLink(mutation.target); continue; } if (mutation.type === 'childList') { for (const node of mutation.addedNodes) { if (!(node instanceof Element)) { continue; } if (node instanceof HTMLAnchorElement) { fixLink(node); } scan(node); } } } }); observer.observe(document.documentElement, { childList: true, subtree: true, attributes: true, attributeFilter: ['href'] }); })(); Brave for desktop can take this script above with no add-ons or plugins. It has native support for "Scriptlets" if Developer Mode is enabled. I figured this out after being annoyed at not being able to clearly see the target URL due to the restructuring of the link with the click tracker. Also as mentioned copying a link to share or bookmark was picking up this BS sovrn url with it depending how it was manipulated. Go to the settings page by pasting this into the URL box: brave://settings/shields/filters Scroll down and toggle on the "Developer Mode" Create custom filter: ar15.com##+js(user-sovrn-direct.js) and Save.Then "Add new scriptlet" and name it: sovrn-direct Then paste in the script from the post I quoted and save all that. Refresh browser...... |
|
Originally Posted By Cobalt135: Brave for desktop can take this script above with no add-ons or plugins. It has native support for "Scriptlets" if Developer Mode is enabled. I figured this out after being annoyed at not being able to clearly see the target URL due to the restructuring of the link with the click tracker. Also as mentioned copying a link to share or bookmark was picking up this BS sovrn url with it depending how it was manipulated. Go to the settings page by pasting this into the URL box: brave://settings/shields/filters Scroll down and toggle on the "Developer Mode" Create custom filter: ar15.com##+js(user-sovrn-direct.js) and Save.Then "Add new scriptlet" and name it: sovrn-direct Then paste in the script from the post I quoted and save all that. Refresh browser...... Thanks! Works in Brave desktop had to copy/paste the code into notepad to make sure it didn't paste in the sovrn links |
|
Originally Posted By Trump45: This version retains the original script's simple purpose but makes it substantially safer and more reliable. Most importantly, it replaces the loose hostname.includes() test with strict domain/subdomain matching, so a domain such as viglink.com.malicious-site.com cannot be mistaken for VigLink. It also safely validates that extracted destinations are genuine http:// or https:// URLs, avoids unnecessarily decoding already-valid URLs, performs case-insensitive parameter matching, and can unwrap several nested affiliate redirects. In addition to scanning the page when it loads, it now watches both new links and existing links whose href is changed later by JavaScript, and it performs another check immediately when a link is clicked. It still uses @grant none, makes no external network requests, loads no outside code, and sends no information anywhere. The original script's basic behavior and scope are preserved while addressing the weaknesses I found in its domain matching, decoding, and dynamic-link handling. (code snipped) 
|
01010111 | 57 | 127 | LXXXVII


|
Originally Posted By DDiggler: Before, users would help out OP with "link made hot." Now, the hotness will be "link left cold" so your browser can autogen the URL link and avoid the tracking. Not.me im.going to.start making.every reply.with a.period in.between every.other pair.of words.in my.post just.to waste.system re.sources
|
|
Or just use Brave browser (and for 100 other reasons) post is from 2021. Make sure to copy and paste it  https://brave.com/privacy-updates/11-debouncing/ protect users against bounce tracking by recognizing when the user is about to visit a known tracking domain, skipping visiting the tracking site all together, and instead directly navigating the user to the intended destination. Bounce Tracking (or, Jerks Refuse to Take “No” for an Answer) Bounce tracking is another technique trackers use to try and violate your privacy and follow you around the Web. Bounce tracking is an attempt to circumvent restrictions on third-party storage in privacy-focused browsers. The technique works by injecting additional sites between a site you’re visiting, and the site to which you intend to navigate. These intermediate sites over time learn what sites you’ve visited, and so can perform the same kinds of tracking sites used to use third-party cookies for. Brave uses a Brave maintained list to identify bounce tracking URLs. This list is maintained by Brave, and is drawn from a mix of crowd-sourcing and existing open-source projects, including the terrific URL Tracking Stripper extension, Link Clearer extension, and Clear URLs extension, along with additional rules maintained by Brave. Brave will maintain this combined list going forward and welcomes collaboration with other similar projects. |

|
Originally Posted By anothermisanthrope: Or just use Brave browser (and for 100 other reasons) post is from 2021. Make sure to copy and paste it https://brave.com/privacy-updates/11-debouncing/ Originally Posted By anothermisanthrope: Or just use Brave browser (and for 100 other reasons) post is from 2021. Make sure to copy and paste it https://brave.com/privacy-updates/11-debouncing/ protect users against bounce tracking by recognizing when the user is about to visit a known tracking domain, skipping visiting the tracking site all together, and instead directly navigating the user to the intended destination. Bounce Tracking (or, Jerks Refuse to Take “No” for an Answer) Bounce tracking is another technique trackers use to try and violate your privacy and follow you around the Web. Bounce tracking is an attempt to circumvent restrictions on third-party storage in privacy-focused browsers. The technique works by injecting additional sites between a site you’re visiting, and the site to which you intend to navigate. These intermediate sites over time learn what sites you’ve visited, and so can perform the same kinds of tracking sites used to use third-party cookies for. Brave uses a Brave maintained list to identify bounce tracking URLs. This list is maintained by Brave, and is drawn from a mix of crowd-sourcing and existing open-source projects, including the terrific URL Tracking Stripper extension, Link Clearer extension, and Clear URLs extension, along with additional rules maintained by Brave. Brave will maintain this combined list going forward and welcomes collaboration with other similar projects. wish all browsers offered this feature. |
"Democracy is two wolves and a lamb voting on what to have for lunch. Liberty is a well-armed lamb contesting the vote."
Necessity is the plea for every infringement of freedom. It is the argument of tyrants; it is the creed of slaves.
Necessity is the plea for every infringement of freedom. It is the argument of tyrants; it is the creed of slaves.

|
Originally Posted By brahm: i am outraged by this. but i don't know what it means other than i am no longer suppose to click links on this site. that is what i have gathered from this thread. This is ridiculous. There's no reason for a site in our privacy-sensitive community to need to track who clicks every link on this site. |
"The state is not the solution. It is the problem." --Javier Milei
"If this is how the state treats its law-abiding citizens, it doesn't deserve to have any"
--Solzhenitsyn
"If this is how the state treats its law-abiding citizens, it doesn't deserve to have any"
--Solzhenitsyn
|
Originally Posted By anothermisanthrope: Or just use Brave browser (and for 100 other reasons) post is from 2021. Make sure to copy and paste it https://brave.com/privacy-updates/11-debouncing/ that's great and all, but Sovrn isn't on their debounce list I still had to paste in the script from above to get brave to work (the mobile app still tries to jump to the sovrn domain) |

|
Originally Posted By AmericaJr: that's great and all, but Sovrn isn't on their debounce list I still had to paste in the script from above to get brave to work (the mobile app still tries to jump to the sovrn domain) Originally Posted By AmericaJr: Originally Posted By anothermisanthrope: Or just use Brave browser (and for 100 other reasons) post is from 2021. Make sure to copy and paste it https://brave.com/privacy-updates/11-debouncing/ that's great and all, but Sovrn isn't on their debounce list I still had to paste in the script from above to get brave to work (the mobile app still tries to jump to the sovrn domain) that's great and all too but: Brave confirms that its default filter set includes EasyPrivacy and uBlock Origin filters, even though some of these aren't necessarily displayed as individually selectable lists in brave://settings/shields/filters. GitHub So if you're asking “What list is responsible for Brave blocking Sovrn?”, the answer is: EasyPrivacy is the primary list to investigate, not the Brave Debouncing list. |
|
Originally Posted By Foxxz: If you use ublock origin you can go into the Configuration / My Filters Check the boxes to enable custom filters and filters requiring trust. Then in the text box below add the following ||sovrn.co/^$urlskip=-blocked ?u Hit the apply changes button. The filter above will rewrite the link when you click on it skipping sovrn.co and going to the original link - your URL bar may show the sovrn.co URL briefly but I did network dumps to verify your browser never actually visits the site. https://www.ar15.com/forums/General/Man-Spikes-Drag-show-punch-bowl-with-Viagra/5-2859630/ Hovering over the date in the twitter box in the OP shows a link directly to x.com Hovering over the x link posted below the twitter box shows a sovrned link While running wireshark, clicking the twitter date shows query in light blue: 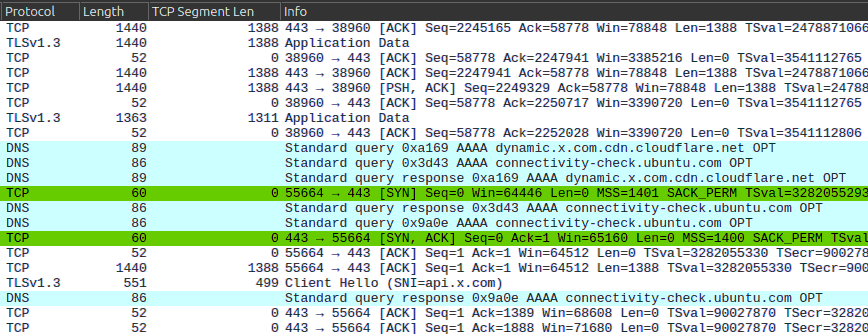 And clicking the sovrned link shows this: 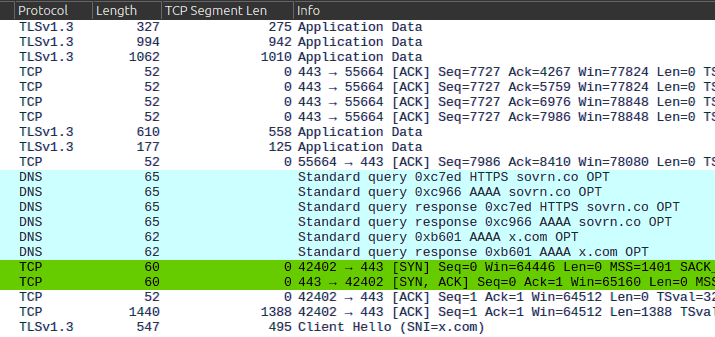 |
Joined:
May 2026
Posts:
1993
EE: 0% (0)
FL, USA
|
Originally Posted By Imzadi: Beyond the ad revenue and the memberships? Originally Posted By Imzadi: Originally Posted By lygxis: Originally Posted By RV8guy: I know I’ll never click on a link here again. Not excusing it but I suspect they're doing it to try and cover tens of thousands in monthly server bills. The possibility that it's likely tied on the back end to ad systems that only pay out because they're collecting information about accounts and people because they think they can make money on that info is just the seedy security disrespecting underside. Beyond the ad revenue and the memberships? Uh ... for the advertisement that change based on who you are (real time bidding / rtb ads) ... that's how those work, in my dime-store understanding. Seems like this expands that from just the affiliate links for whatever they limted it to before, to *every single user posted link on the forum.* If advertisers didn't percieve that the information generated when someone clicks a link wasn't useful enough to create a personalized targettable ad, they wouldn't pay for it. It turns every one of those links into a possible tiny revenue stream. |
Joined:
May 2026
Posts:
1994
EE: 0% (0)
FL, USA
|
Originally Posted By MongooseKY: I'm using TamperMonkey with the following script to eradicate sovrn, vigilink, and avantlink redirects across the board. I'm sick and tired of being monetized by having everything I click routed through third parties who aren't accountable for the crap they do. // ==UserScript== // @name Remove VigLink, AvantLink, and Sovrn Redirects // @namespace https://tampermonkey.net/ // @version 1.0 // @description Strip redirect wrappers from VigLink, AvantLink, and Sovrn links // @match *://*/* // @run-at document-end // @grant none // ==/UserScript== (function() { 'use strict'; const REDIRECT_DOMAINS = [ "viglink.com", "redirect.viglink.com", "avantlink.com", "www.avantlink.com", "sovrn.co", "redirect.sovrn.com" ]; const PARAM_CANDIDATES = [ "url", "u", "dest", "destination", "to", "afsrc", "redir", "r" ]; function extractRealUrl(href) { try { const parsed = new URL(href); // Check if this is a redirector domain if (!REDIRECT_DOMAINS.some(d => parsed.hostname.includes(d))) { return null; } // Try all known parameter names for (const p of PARAM_CANDIDATES) { let val = parsed.searchParams.get(p); if (val) { // Some redirectors double-encode URLs try { val = decodeURIComponent(val); } catch {} try { val = decodeURIComponent(val); } catch {} // Validate it's a real URL if (val.startsWith("http://") || val.startsWith("https://")) { return val; } } } return null; } catch (e) { console.error("Redirect fix error:", e); return null; } } function fixLink(a) { if (!a || !a.href) return; const real = extractRealUrl(a.href); if (real) { console.log("Rewriting URL: " + a.href + " as " + real); a.href = real; } } function scan() { document.querySelectorAll("a[href]").forEach(fixLink); } // Initial scan scan(); // Watch for dynamically added links const observer = new MutationObserver(mutations => { for (const m of mutations) { for (const node of m.addedNodes) { if (node.nodeType === 1) { if (node.tagName === "A") { fixLink(node); } else { node.querySelectorAll?.("a[href]").forEach(fixLink); } } } } }); observer.observe(document.body, { childList: true, subtree: true }); })(); If you're maniacal and dont' mind having to manually enter web addresses, temp containers plus and configure the settings so that when you get bounced to a different domain, even if t he final destiation is thte original domain you came from, it sends it to a new tab with all the history and cookies and etc stripped out. I can't tell you how many sites I run into that try and do that "bounce you to a tracking domain when you click links that should stay on the site" trick. It has gotta suck to try and run any server that gets heavy usage these days, the entire internet is built for plug and play monetization that *screws the daylights out of the endusers.* I wonder how high usage sites manage to keep afloat without being skeezy. Last thing I want to see is the cockroaches from verticalscope scoop up arf. |

|
Originally Posted By way: Want this to work so bad, but I visited the drag show viagra link in Firefox running the above filter in uBlock https://www.ar15.com/forums/General/Man-Spikes-Drag-show-punch-bowl-with-Viagra/5-2859630/ Hovering over the date in the twitter box in the OP shows a link directly to x.com Hovering over the x link posted below the twitter box shows a sovrned link While running wireshark, clicking the twitter date shows query in light blue: https://i.postimg.cc/L8QmnsWv/standard-query.png And clicking the sovrned link shows this: https://i.postimg.cc/cLCSySJN/sovrn-query.png Yes it still does a DNS lookup for sovrn but it is NOT connecting to their server. Not only did I verify this by watching network traffic, but I blocked DNS and even sent a DNS response for sovrn to 127.0.0.1 and my honeypot server. Zero hits. I have confirmed In multiple ways that my URL rewrite works. |
|
Originally Posted By SimonPhoto: Well, it means for the first time in two decades I'm probably not going to renew my team account. This is ridiculous. There's no reason for a site in our privacy-sensitive community to need to track who clicks every link on this site. Kind of funny that they “purge” usernames from archive searches to “protect users’ privacy,” but sell out said posters a fraction of a penny at a time to companies that build detailed profiles on us. Is there any solution for Brave mobile iOS? |
|
Originally Posted By Foxxz: Yes it still does a DNS lookup for sovrn but it is NOT connecting to their server. Not only did I verify this by watching network traffic, but I blocked DNS and even sent a DNS response for sovrn to 127.0.0.1 and my honeypot server. Zero hits. I have confirmed In multiple ways that my URL rewrite works. Originally Posted By Foxxz: Originally Posted By way: Want this to work so bad, but I visited the drag show viagra link in Firefox running the above filter in uBlock https://www.ar15.com/forums/General/Man-Spikes-Drag-show-punch-bowl-with-Viagra/5-2859630/ Hovering over the date in the twitter box in the OP shows a link directly to x.com Hovering over the x link posted below the twitter box shows a sovrned link While running wireshark, clicking the twitter date shows query in light blue: https://i.postimg.cc/L8QmnsWv/standard-query.png And clicking the sovrned link shows this: https://i.postimg.cc/cLCSySJN/sovrn-query.png
|
|
Originally Posted By NachoDip: Or you could just send it to people who want it. Originally Posted By NachoDip: Originally Posted By AmorphousBlob: Heh, it's just something I vibed coded with codex. You can see most of the original source in this thread: https://www.ar15.com/forums/General/I-vibe-coded-an-extension-to-hide-users-on-arf/5-2849671/. It's not released anywhere. Honestly if you spent 20 minutes with your favorite LLM I'm betting you could make something as good or better. Or you could just send it to people who want it. And then have them bug him anytime it breaks? Fuck that. If they're too tarded to do it themselves then why would he want them as customers for no money? |
Joined:
Feb 2024
Posts:
2297
EE: 0% (0)
USA
|
Originally Posted By Echd: Given it's going to fingerprint you and your online activity to arfcom at some level it's probably more meaningful than driving past a flock camera lol. Can you explain this to me like I'm a 6th grader please Exactly what info do these links send? This is kinda concerning being that most of the membership here own guns and the info can be useful for LE agencies, and the fact that a large part of the membership here are LEO's.... |
Joined:
Feb 2024
Posts:
2298
EE: 0% (0)
USA
|
Originally Posted By Foxxz: Yes it still does a DNS lookup for sovrn but it is NOT connecting to their server. Not only did I verify this by watching network traffic, but I blocked DNS and even sent a DNS response for sovrn to 127.0.0.1 and my honeypot server. Zero hits. I have confirmed In multiple ways that my URL rewrite works. So that is normal when running the above script? |

|
Originally Posted By Tokamak: I did the Brave script and when i hover over a hyperlink, it still shows sovern. before the actual link. So that is normal when running the above script? In Brave, go to brave://settings/shields/filters. Enable toggle for Developer Mode. Hit "Add New Scriptlet" button at bottom of page. Copy/Paste script, type sovrn-direct in name block and save. Brave will save as user-sovrn-direct.js Attached File In the Create custom filters block, input ar15.com##+js(user-sovrn-direct.js) and hit the Save changes button. Attached File When you refresh the Arf tab the sovrn links should be gone. |
Originally Posted By HermanSnerd:
In reality, those two hot chicks that you just met that want you to come home with them for "a good time", are merely the bait for the huge guy hiding in the closet wearing a Batman suit.
In reality, those two hot chicks that you just met that want you to come home with them for "a good time", are merely the bait for the huge guy hiding in the closet wearing a Batman suit.
Why are all links in GD going through sovrn.co now? (Page 2 of 2)
Join the Community
Your next conversation starts here.
Create your free account to join discussions, share your experience, save topics, and connect with the AR15.COM community.
- Join discussions
- Follow topics and replies
- Connect with fellow enthusiasts
Already a member? Sign in
Stay informed by subscribing to our Newsletter